Jun 2023
Sabermetrics and Cyber Risk Quantification
What baseball’s sabermetrics revolution teaches us about quantifying cyber risk.
Wait, what?
Two of my passions — baseball and cybersecurity — might seem worlds apart, but they share a similar trajectory towards quantifying the probability of events. In this post, I’ll share some history about Sabermetrics, and how we can relate it’s rise to where risk quantification will take us in cybersecurity.
Sabermetrics: Transforming Baseball with Numbers
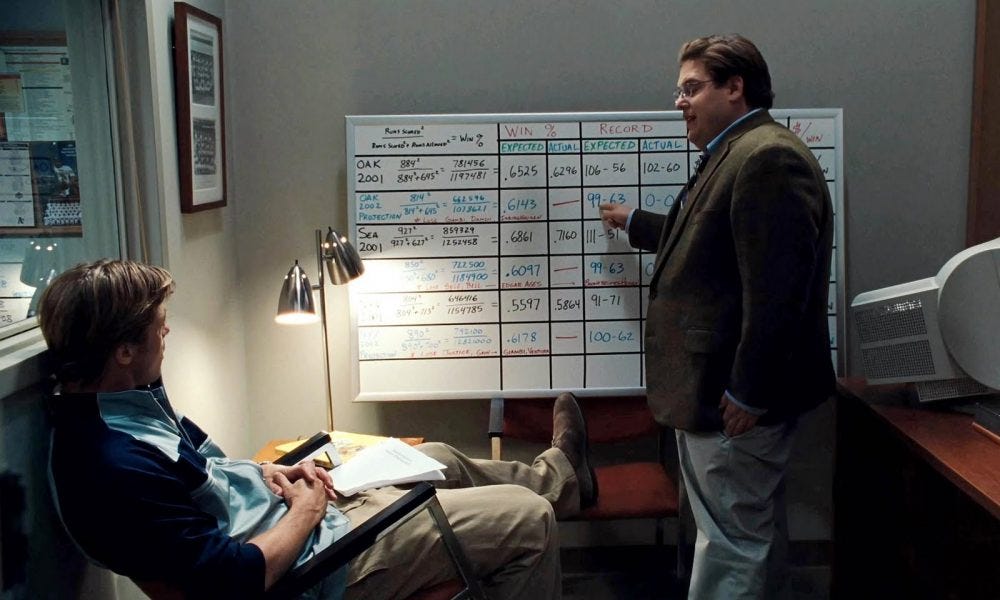
Sabermetrics — named after the Society for American Baseball Research (SABR) — is the empirical analysis of baseball. Its history and evolution is a testament to the ever-growing love for baseball and the human drive for understanding and predicting performance.
The early roots of Sabermetrics can be traced back to the 19th century when Henry Chadwick, an English cricket journalist and baseball pioneer, introduced batting averages and earned run averages. But the modern revolution began in the 1970s with the work of Bill James, who coined the term. James, a baseball writer and historian, popularized the concept of using statistics to understand and predict baseball performance.
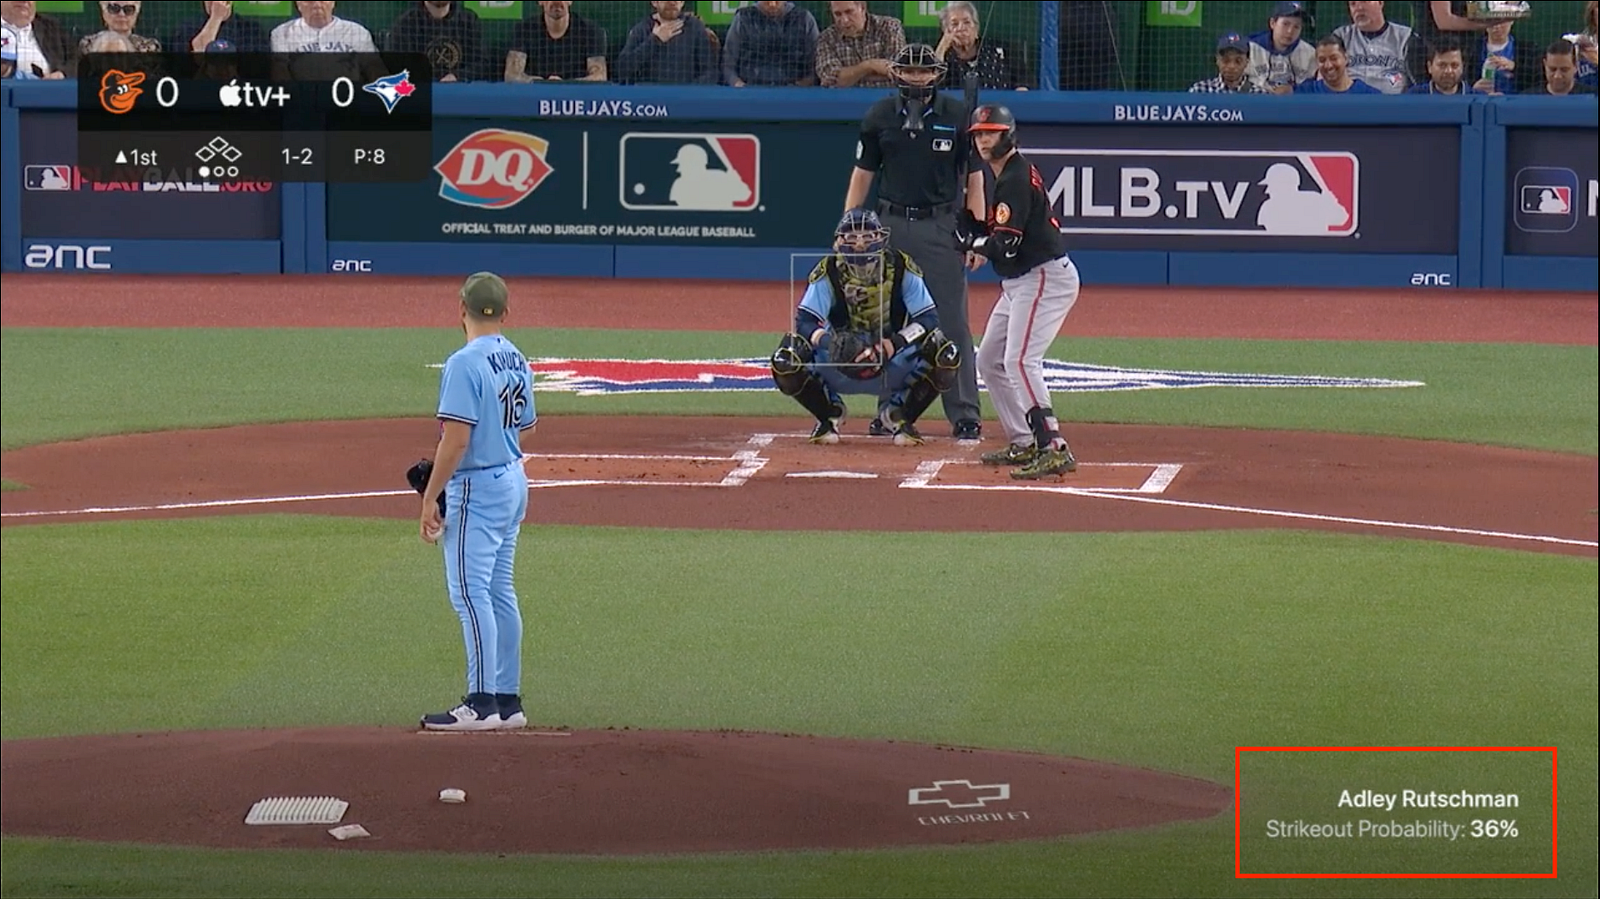
Over the decades, Sabermetrics has evolved from simple stats to complex metrics like Wins Above Replacement (WAR), On-base Plus Slugging (OPS), and Fielding Independent Pitching (FIP). It has changed the way teams scout, evaluate and pay players, the strategies managers use in games, and fundamentally how we understand the sport (See Statcast). We’ve even seen event probabilities feature on Apple TV+ broadcasts of games. I won’t dive into the integration of sports betting here, but the way Apple presents these probabilities on screen signals baseball’s quantification becoming the norm.
Cyber Risk Quantification: Turning Cybersecurity up to 11
Classic vulnerability management often relies solely (or mostly) on CVSS (Common Vulnerability Scoring System) scores, which are statistically invalid — you can’t add ordinal scales together to produce any result of value. As a result, without a solid framework for assessing and quantifying risk, cybersecurity has often been viewed as a black box and a major cost center.
As discussed in a recent post on the Resilient Cyber blog, Chris Hughes touches on the need to develop new ways to manage the risks presented by the meteoric rise in CVEs reported year over year (25K+ reported into the NVD in 2022 alone, with 2023 on pace to exceed this by 13%). I don’t think the industry can keep up with SLAs (Service Level Agreements) that are heavily weighted or entirely defined by CVSS scores, which is driving the need for a more data-driven, analytical approach to cybersecurity. Enter Cyber Risk Quantification — a discipline designed to objectively assess and quantify cyber risk, as well as provide some predictive analytics to anticipate events.
Newer frameworks, ideas, and data aggregation sources, such as EPSS and KEV, suggest that we need to be more analytical when thinking about security. Firms are beginning to realize that the old methods frankly do not appropriately mitigate risk, and are moving towards solutions that provide the necessary context to build models and make informed decisions, like Security Data Lakes.
The rise of Cyber Risk Quantification is changing that, allowing organizations to quantify potential risk in monetary terms, based on industry and internal data, and make informed decisions on risk mitigation investments. The discipline continues to evolve, adopting machine learning and AI techniques to analyze patterns and predict future threats.
Blending Disciplines: A Shared Journey to Derive Value
Both Sabermetrics and Cyber Risk Quantification represent the human drive to understand, predict, and influence outcomes through data and analysis. They both rely heavily on data-driven decision-making, predictive modeling, evidence-based strategies, risk assessment, and continuous improvement to derive the same thing: value.
Having played baseball growing up, as well as dabbling in managing a team (both in real life and Rotisserie League), I’ve always sought out ways to strategize how to best achieve the desired output of a game/season: a win/championship. Delving into The Book: Playing the Percentages in Baseball taught me that certain managerial concepts, like playing baseball using common misconceptions such as your best hitter batting cleanup, doesn’t always heed desired outcomes as demonstrated by our vast historical statistical record of baseball. This is also true in cybersecurity.
The evolution of Sabermetrics and Cyber Risk Quantification showcases the transformative power of data and analytics. By studying their histories and the paths they’ve taken, we can better understand the power of data in shaping our future in sports, cybersecurity, and humanity.
Further Reading
If you liked this and you’re interested in further reading about either of these topics, I highly recommend the following books: